Connect AI supports SSO with multiple identity providers. To enable SSO for your account, contact CData Support.
CData Support initiates the SSO setup and provides the callback URL that you must register in your identity provider. After you register the application and gather the required credentials, send them to CData Support to complete the configuration. CData Support handles the broker-side setup (Auth0 configuration, rules, and routing). You do not handle those directly.
For more information about configuring SSO, refer to Single Sign-On in the Auth0 documentation.
SSO User Provisioning (Without JIT)
SSO handles authentication only. Before a user can sign in via SSO, they must have a Connect AI account. Without JIT provisioning enabled, an Administrator must invite the user by email first. See Users for details.
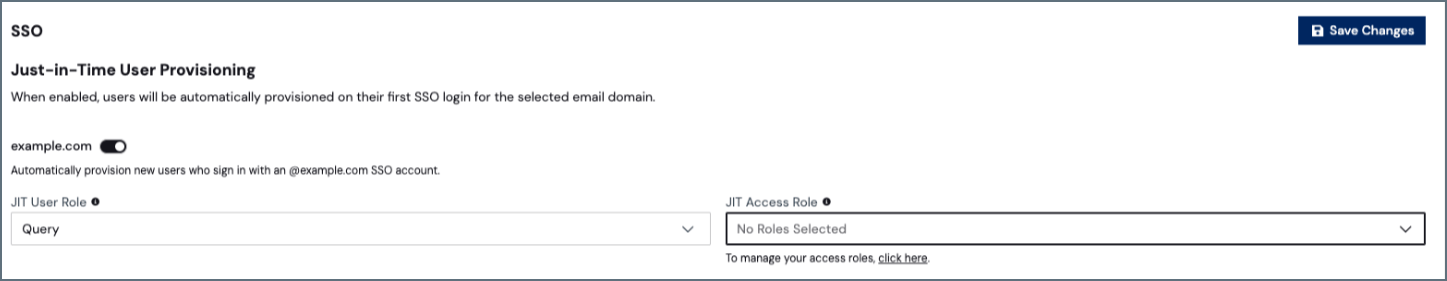
JIT User Provisioning
Your account must already have SSO configured to enable JIT provisioning.
Troubleshooting
For common questions and errors for each SSO provider, see the following troubleshooting guides: